Adobe Commerce and Magento Open Source are affected by a critical vulnerability tracked as CVE-2025-54236, also called “SessionReaper”. Adobe released an out-of-band fix on 9 September 2025 under Security Bulletin APSB25-88. On Tap began deploying the fix to client environments shortly after its release.
Here is what merchants need to know about the vulnerability, Adobe’s response, and the steps to protect their stores.
What is SessionReaper (CVE-2025-54236)?
SessionReaper is an improper input validation vulnerability in Adobe Commerce and Magento Open Source. Adobe’s security bulletin classifies its impact as a security feature bypass and gives it a critical CVSS score of 9.1. An attacker does not need to log in or persuade a customer to take action to attempt exploitation.
For merchants, the concern is that a successful attack could give an unauthorised person access to customer accounts and the information available through them.
Why is SessionReaper critical?
The vulnerability can be exploited without an account or customer interaction. Security researcher Sansec reports that customer-account takeover is possible and that remote code execution could occur under certain conditions. Adobe’s bulletin describes the vulnerability’s impact as a security feature bypass.
The risk calls for prompt action, even if a store shows no obvious signs of compromise. Applying the fix closes the identified vulnerability; checking for suspicious activity helps merchants establish whether further investigation is needed.
On Tap began deploying the fix to client environments shortly after Adobe’s release, with checks covering affected storefront functions, custom code, and integrations.
Affected Magento/Adobe Commerce versions
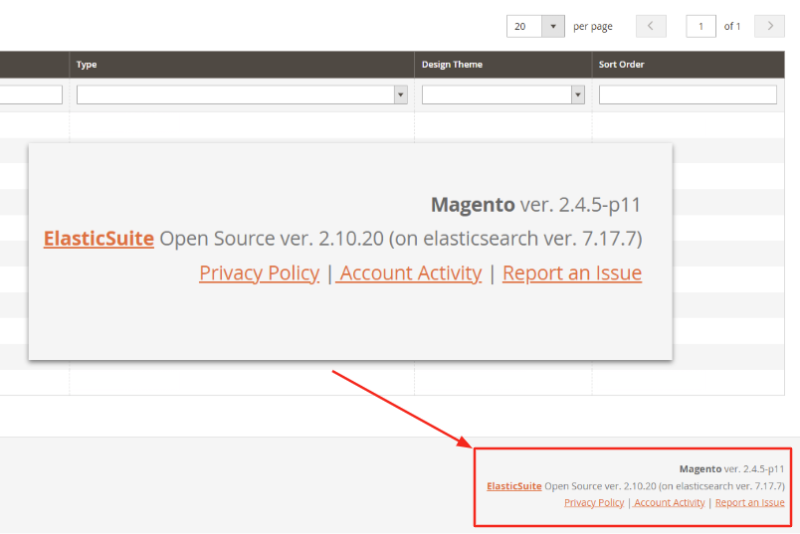
Adobe’s bulletin lists the following affected versions:
|
Product |
Affected versions |
|
Adobe Commerce |
2.4.9-alpha2 and earlier; 2.4.8-p2 and earlier; 2.4.7-p7 and earlier; 2.4.6-p12 and earlier; 2.4.5-p14 and earlier; 2.4.4-p15 and earlier |
|
Adobe Commerce B2B |
1.5.3-alpha2 and earlier; 1.5.2-p2 and earlier; 1.4.2-p7 and earlier; 1.3.4-p14 and earlier; 1.3.3-p15 and earlier |
|
Magento Open Source |
2.4.9-alpha2 and earlier; 2.4.8-p2 and earlier; 2.4.7-p7 and earlier; 2.4.6-p12 and earlier; 2.4.5-p14 and earlier |
Check your installed edition and version against the bulletin before choosing a remediation route.
Adobe’s emergency response to the issue
Adobe released the out-of-band VULN-32437-2-4-X hotfix to address CVE-2025-54236. This gave affected merchants a way to address the vulnerability without waiting for the next scheduled security release.
Merchants should follow Adobe’s instructions for their installed version and verify that the fix has been applied successfully. A web application firewall (WAF) can provide an additional layer of protection, but it does not replace the software fix.
What merchants should do?
-
Apply Adobe’s fix promptly: Check your installed version, deploy the applicable hotfix, and confirm that it is active in the production environment.
-
Test the store after deployment: Check checkout, customer accounts, custom code, and third-party integrations. Monitor for unexpected behaviour so that compatibility issues can be identified and resolved.
-
Use WAF protection as an additional measure: If patch deployment is delayed, review the protection available for your environment, including Adobe Commerce Cloud’s Fastly configuration or a service such as Sansec Shield. Do not rely on WAF protection in place of the hotfix.
-
Review possible exposure: If the store was vulnerable, On Tap recommends examining logs and signs of compromise. Investigate suspicious activity and rotate credentials or cryptographic keys if the investigation indicates they may have been exposed. These are risk-based incident response steps in addition to applying Adobe’s fix.
Continue to follow Adobe’s security bulletins for guidance relevant to your environment.
Final notes
SessionReaper (CVE-2025-54236) highlights the importance of timely security updates, deployment testing, and incident response preparation for Adobe Commerce and Magento Open Source stores. The priority is to apply and verify Adobe’s fix, then investigate any signs of compromise.
On Tap’s Magento expert team can help with hotfix deployment and testing while minimising disruption. We also offer AuditIQ for ongoing security and performance monitoring. Contact us if you need help securing your store.