 Best full-service eCommerce agency 2026
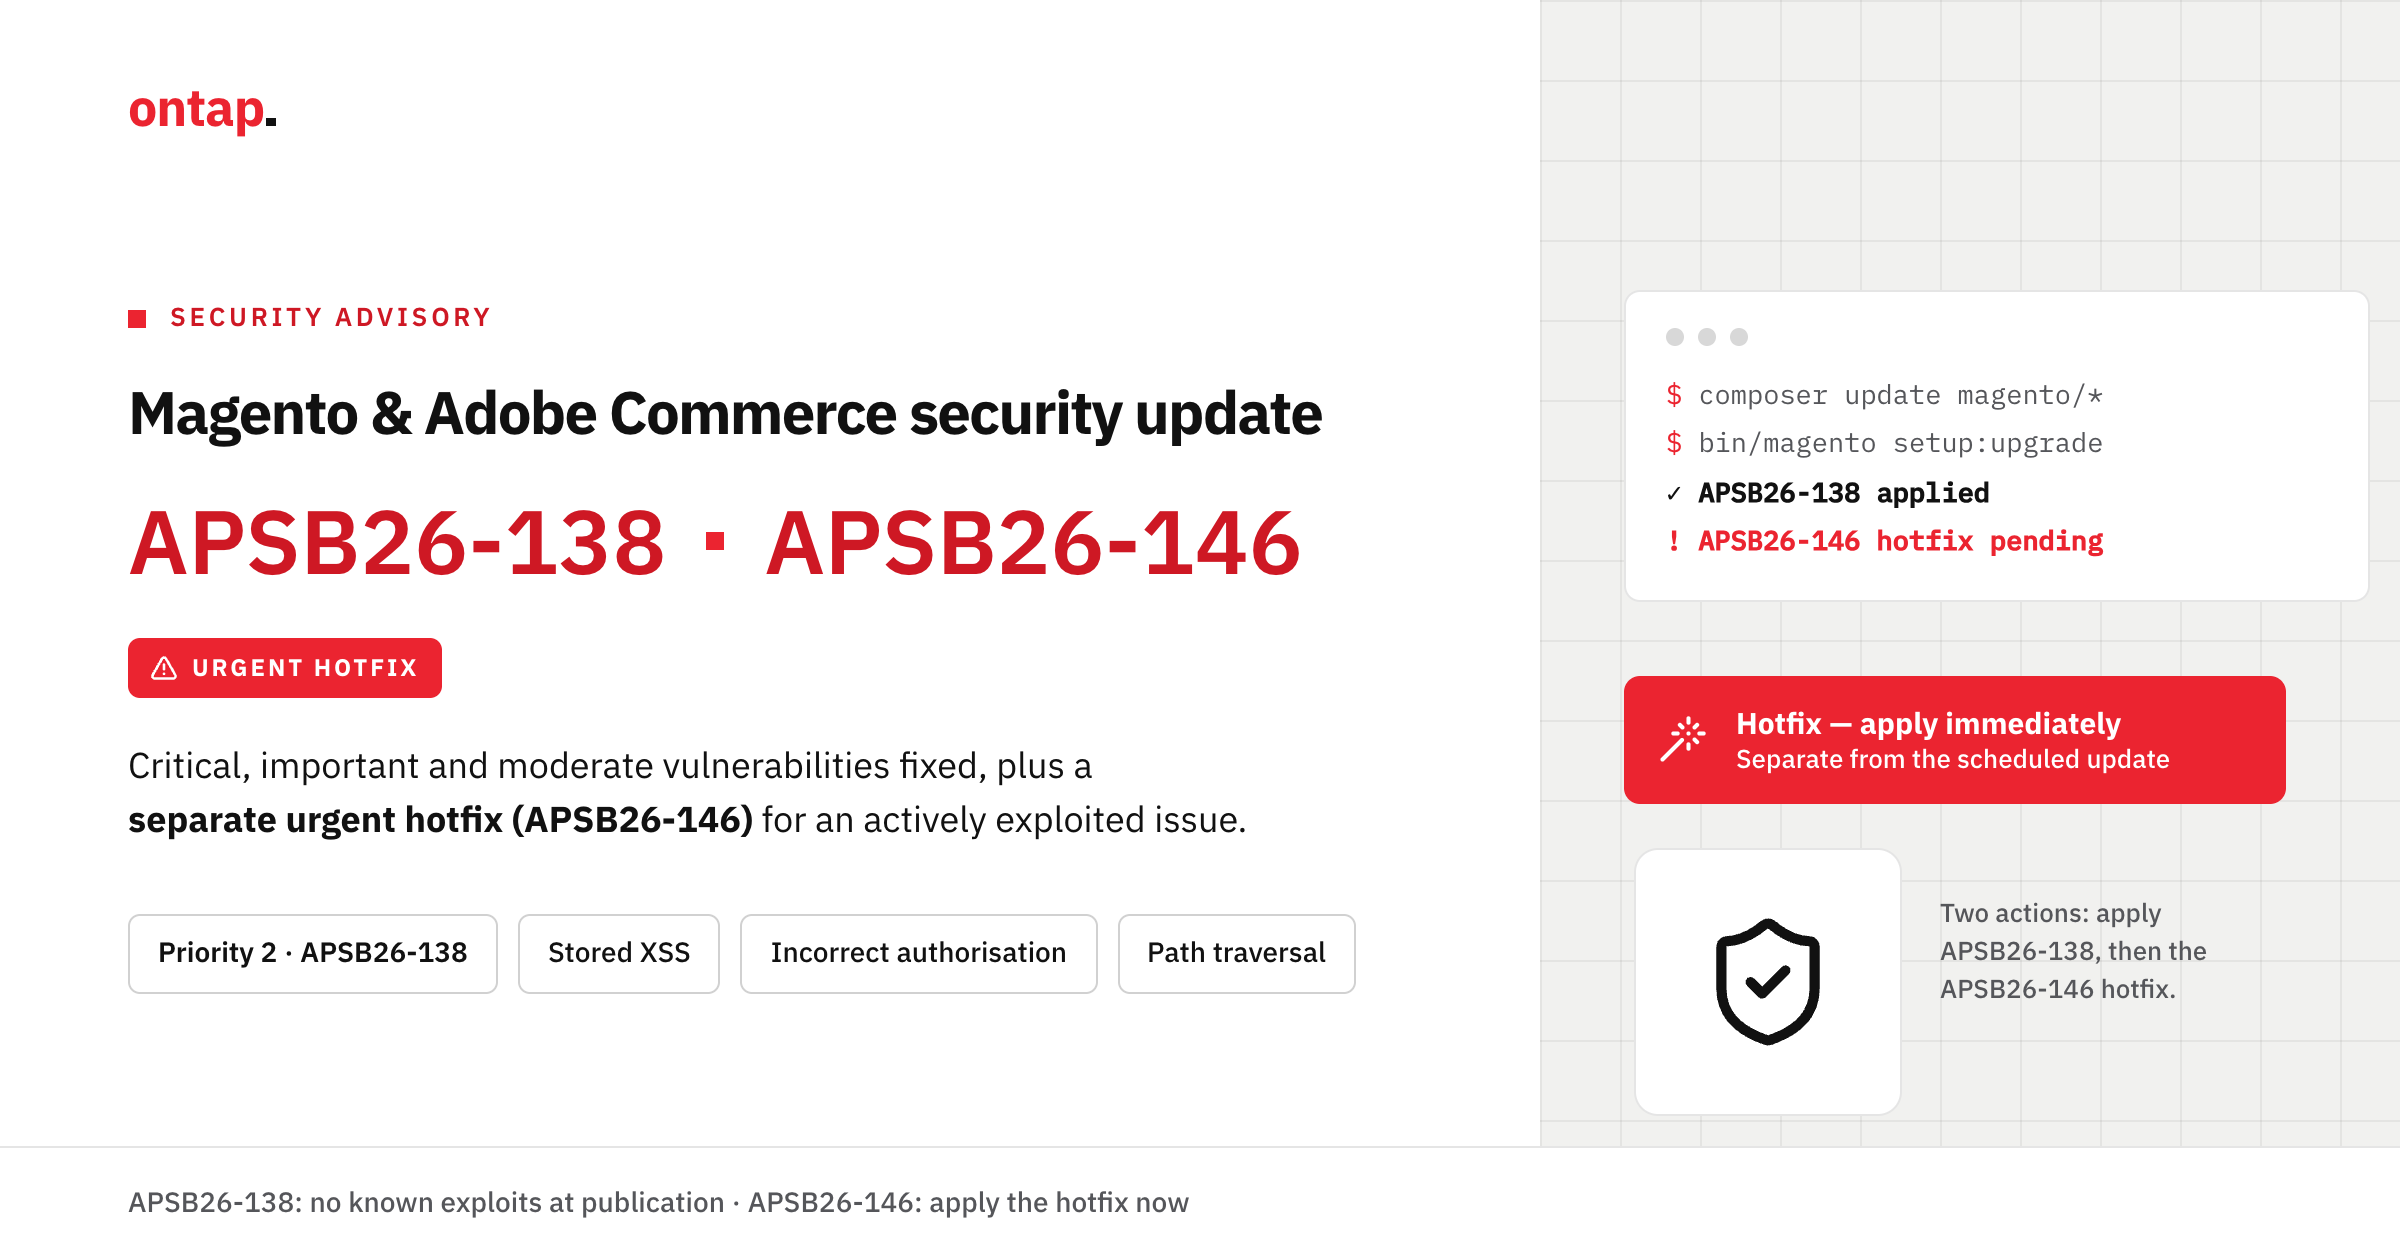
On 8 September 2026, Adobe released APSB26-138, a scheduled security update for Adobe Commerce and Magento Open Source. Its vulnerability table lists eight issues, each rated Critical.
A day earlier, Adobe released the separate APSB26-146 bulletin for CVE-2026-75650. Adobe scored the vulnerability CVSS 10.0 and said it was being exploited in the wild. The APSB26-146 hotfix is separate from the September fixes for APSB26-138. Affected merchants need to address both.
Here is what the two bulletins cover, which versions are affected, and where to find Adobe’s patch instructions.
What happened, in simple terms
APSB26-138: the scheduled update
APSB26-138 addresses vulnerabilities in Adobe Commerce, Adobe Commerce B2B and Magento Open Source. Depending on the issue, successful exploitation could allow privilege escalation or bypass a security control. Two stored cross-site scripting vulnerabilities have CVSS scores of 9.3. They do not require authentication to exploit, although their published CVSS vectors include user interaction.
When Adobe published the bulletin, it said it was not aware of exploitation in the wild for the issues covered by APSB26-138. That statement does not apply to the separate CVE-2026-75650 issue.
The affected release lines and component versions are listed below. Check the precise version of each component installed on your store before selecting a patch.
APSB26-146: the separate hotfix
APSB26-146 addresses CVE-2026-75650, which could allow an unauthenticated attacker to execute arbitrary code on an affected installation. Adobe rated it Critical, scored it CVSS 10.0, and reported exploitation in the wild when it published the bulletin on 7 September.
The September APSB26-138 fixes do not replace the separate CVE-2026-75650 hotfix. Apply the hotfix as soon as possible and follow Adobe’s installation instructions for both fixes.
What's in the APSB26-138 patch?
Bulletin summary
-
Bulletin ID: APSB26-138
-
Published: 8 September 2026
-
Adobe priority rating: 2
-
Potential impact: Security feature bypass and privilege escalation
Adobe’s priority rating indicates how it recommends scheduling an update. It is separate from the severity and CVSS score assigned to an individual vulnerability.
Affected versions
|
Adobe Commerce |
Adobe Commerce B2B |
Magento Open Source |
|
2.4.9-2026-aug and earlier 2.4.8-2026-aug and earlier 2.4.7-2026-aug and earlier 2.4.6-2026-aug and earlier 2.4.5-2026-aug and earlier 2.4.4-2026-aug and earlier |
1.5.3-2026-aug and earlier 1.5.2-2026-aug and earlier 1.4.2-2026-aug and earlier 1.3.4-2026-aug and earlier 1.3.3-2026-aug and earlier |
2.4.9-2026-aug and earlier 2.4.8-2026-aug and earlier 2.4.7-2026-aug and earlier 2.4.6-2026-aug and earlier |
Adobe lists all platforms for these affected versions. Check the bulletin’s version table alongside your installed Commerce and B2B component versions.
Magento Open Source 2.4.6 needs particular attention: Adobe lists it as affected, but the bulletin’s updated-version table for Magento Open Source begins at 2.4.7. Merchants on 2.4.6 should confirm their upgrade and patch path with their development team rather than assume a September APSB26-138 patch is available for that release line. The separate APSB26-146 hotfix instructions must also be checked for the installed version.
Vulnerability details
Adobe disclosed eight vulnerabilities in APSB26-138. Each is rated Critical in its vulnerability table:
|
Category |
Impact |
Severity |
CVSS |
CVE |
|
Stored cross-site scripting (CWE-79) |
Privilege escalation |
Critical |
9.3 |
CVE-2026-76200 |
|
Stored cross-site scripting (CWE-79) |
Privilege escalation |
Critical |
9.3 |
CVE-2026-76201 |
|
Incorrect authorisation (CWE-863) |
Security feature bypass |
Critical |
8.7 |
CVE-2026-77111 |
|
Incorrect authorisation (CWE-863) |
Privilege escalation; B2B |
Critical |
8.6 |
CVE-2026-77109 |
|
Incorrect authorisation (CWE-863) |
Security feature bypass |
Critical |
8.6 |
CVE-2026-77774 |
|
Incorrect authorisation (CWE-863) |
Privilege escalation |
Critical |
8.2 |
CVE-2026-76202 |
|
Path traversal (CWE-22) |
Security feature bypass |
Critical |
7.6 |
CVE-2026-77110 |
|
Incorrect authorisation (CWE-863) |
Privilege escalation; B2B |
Critical |
7.5 |
CVE-2026-77108 |
CVSS is a standardised measure of a vulnerability’s technical severity. Adobe identifies CVE-2026-77109 and CVE-2026-77108 as B2B issues. Its bulletin credits independent researchers 0x0.eth, wohlie, and e0x1337 for reporting several of the vulnerabilities. The full vulnerability table includes authentication requirements and CVSS details for each CVE.
How to patch
Adobe’s APSB26-138 bulletin lists the following September updated-version labels:
-
Adobe Commerce: 2.4.9-2026-sep, 2.4.8-2026-sep, 2.4.7-2026-sep, 2.4.6-2026-sep, 2.4.5-2026-sep and 2.4.4-2026-sep
-
Adobe Commerce B2B: 1.5.3-2026-sep, 1.5.2-2026-sep, 1.4.2-2026-sep, 1.3.4-2026-sep and 1.3.3-2026-sep
-
Magento Open Source: 2.4.9-2026-sep, 2.4.8-2026-sep and 2.4.7-2026-sep
Adobe supplies installation instructions and isolated security patch files. The appropriate file depends on the release line, patch level and components installed on your store.
Before applying a file, check Adobe’s stated prerequisites for your version and whether earlier monthly security patches are required. Adobe Commerce on Cloud infrastructure merchants should also check the relevant Cloud Patches release before applying a patch manually.
Verifying you're protected
After installation, ask your development team to confirm that the required APSB26-138 fixes are present for your release line and installed components. Adobe’s patch instructions describe available checks.
Verify the CVE-2026-75650 hotfix separately. Confirming that the APSB26-138 fixes have been applied does not establish that the separate hotfix is in place.
The APSB26-146 hotfix
-
Bulletin ID: APSB26-146
-
CVE: CVE-2026-75650
-
Adobe priority rating: 1
-
Severity: Critical
-
CVSS score: 10.0
-
Authentication required to exploit: No
-
Potential impact: Arbitrary code execution
-
Status reported by Adobe: Exploited in the wild
The CVE-2026-75650 hotfix is separate from the September APSB26-138 security fixes. Use Adobe’s version-specific hotfix instructions to select the appropriate file and confirm that it has been applied. Check the current instructions when carrying out remediation, as Adobe can revise its installation guidance.
Bottom line
APSB26-138 and APSB26-146 address separate security issues. Check your installed versions, follow Adobe’s instructions for the relevant September fixes and the CVE-2026-75650 hotfix, then verify both. Give the hotfix prompt attention because Adobe reported active exploitation when it published APSB26-146.
On Tap’s Evergreen programme supports ongoing Adobe Commerce and Magento maintenance. If you need help identifying the right patches, applying them or checking your store’s status, contact On Tap.